Cybersecurity
Your shield in the digital world.
We protect your data, systems, and peace of mind.
Our Mission
Our mission is to enable organizations to be resilient and secure, and to support them through our expertise in risk assessment, validation, and compliance services. We deliver strategic guidance and rigorous testing to ensure our clients' digital environments are secure, compliant, and prepared for evolving cyber threats — empowering them to operate with confidence and trust.
Our Vision
To be a trusted global partner in cybersecurity — enabling organizations to thrive in a secure digital world by delivering innovative, reliable, and future-ready security solutions that protect what matters most.
Architecture
Cybersecurity Architecture & Engineering
- Cybersecurity architecture design, engineering, implementation, and maintenance with compliance to IEC 62443, ISO 27001 and ISO 27002.
- Network security architecture review and firewall configurations and installations.
- Industrial and enterprise firewall configuration and management with industrial best practices.
- System, network, and product hardening using CIS (Center for Internet Security) benchmarks.
- Secure design practices following a defense-in-depth strategy.
Compliance
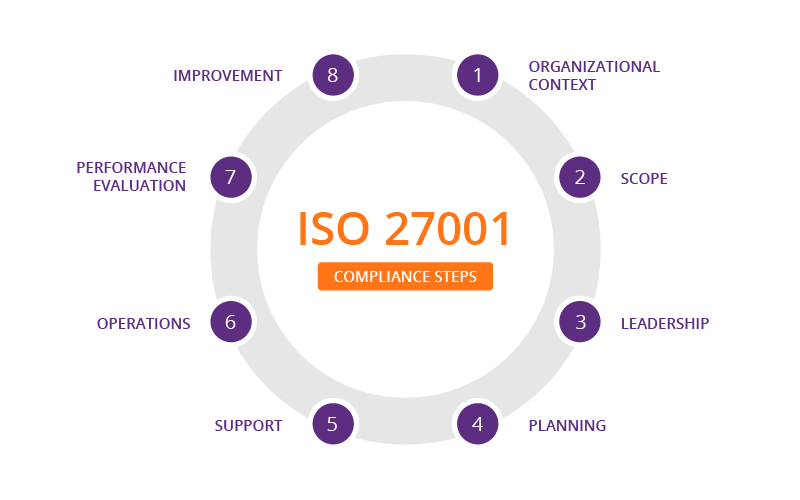
Standards & Compliance
- Establishment of Cybersecurity Management Systems (CSMS) for OT and IT industries.
- Compliance support for IEC 62443, ISO 27001/27002/27005, ISO 21434, NIST, and local regulations.
- Country-specific cybersecurity compliance (e.g. KSA-NCA, EU-CRA/NIS, Australia-AS777, NERC-CIP, IEC 62351).
- Compliance audits, assessments, and cybersecurity validation.
Risk Management
Risk Assessment and Management
- Risk assessment per ISO 27005, IEC 62443, and NIST SP 800-82.
- Threat modeling and cybersecurity posture evaluation.
- Cybersecurity posture assessment.
- Gap analysis.
- Compliance mapping.
- Security control validations.
- Selection of cybersecurity control measures.
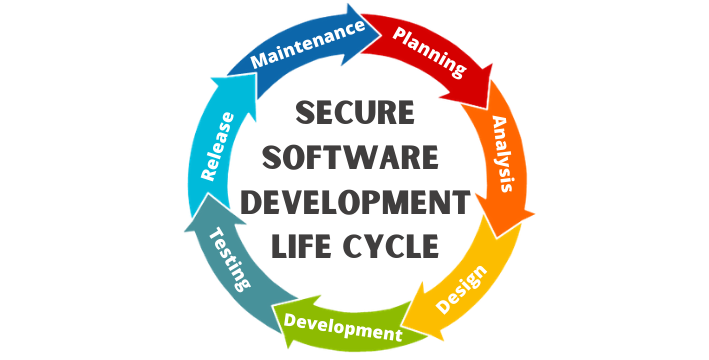
Secure Development
Secure Development & Product Security
- Secure product development guidelines and support.
- Embedded product cybersecurity evaluation and assessment.
- Guidance and support for the secure development life cycle.
Development
Supplier Development for Cybersecurity
- Supplier cybersecurity development programme in line with IEC 62443-4-1 & IEC 62443-4-2.
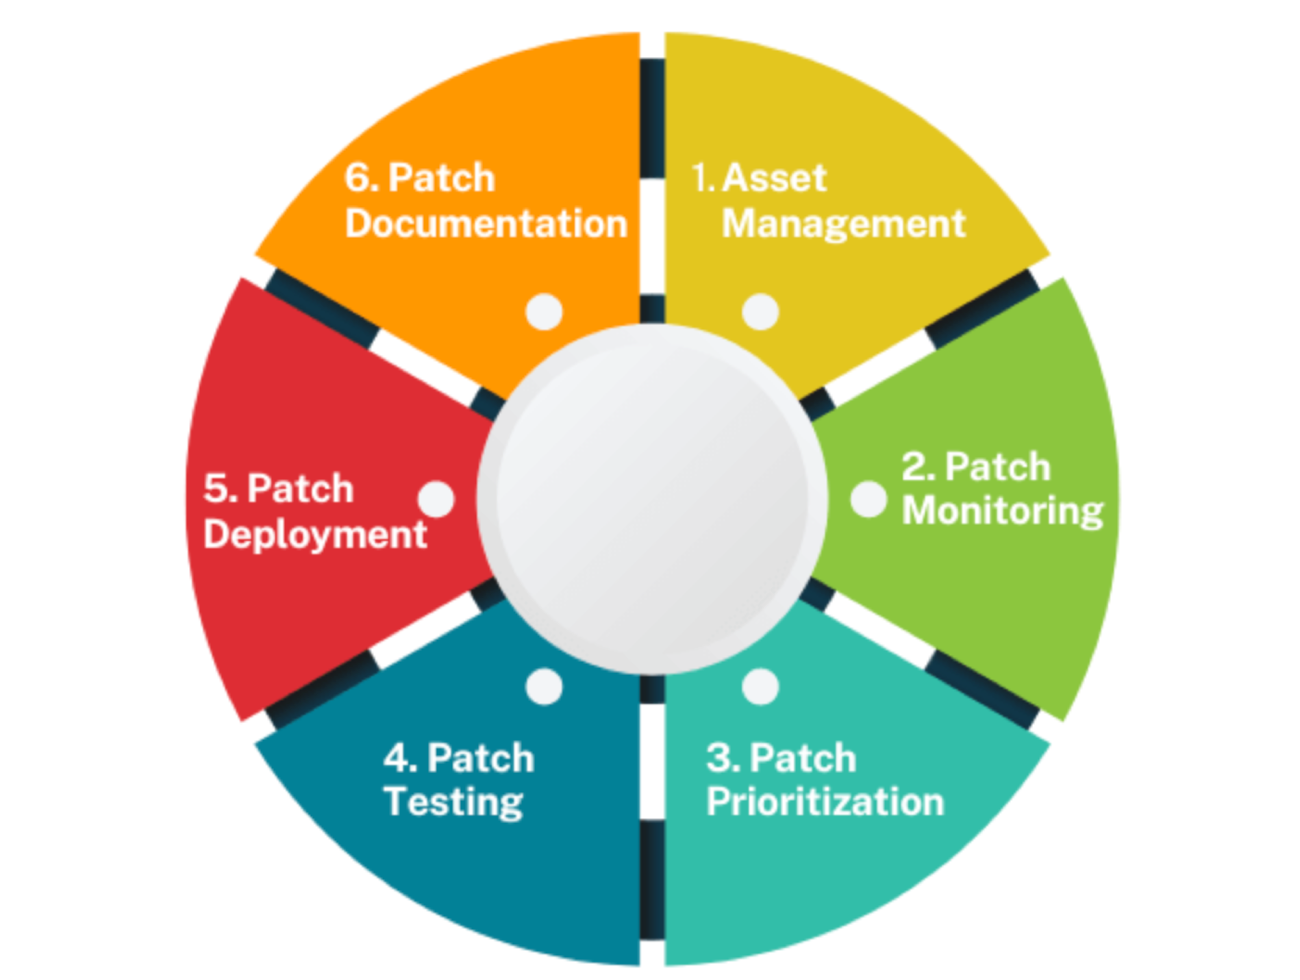
Asset Management
Asset & Patch Management
- Asset inventory classification and management.
- Microsoft patch validation and patch management for IT and OT systems.
- Vulnerability and patch management with remediation recommendations.
- Managing security configurations.
- PKI certificate management.
Detection
Detection & Response
- IDS / IPS setup, configuration and deployment.
- SIEM support.
- Incident management and handling.
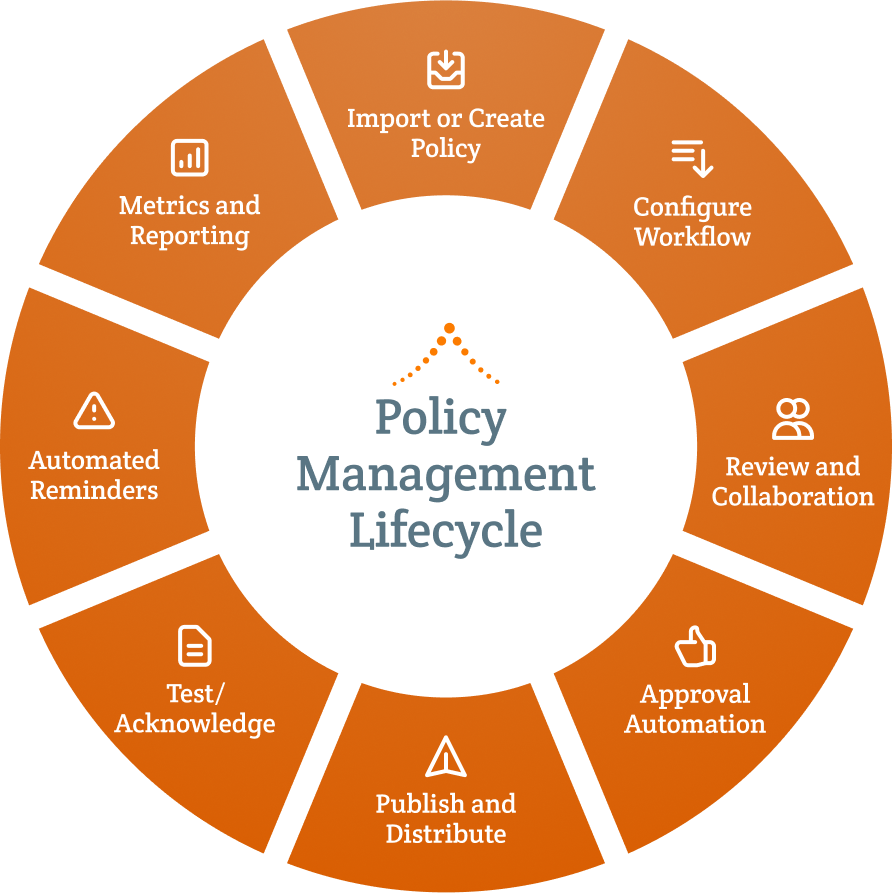
Policy Management
Requirements & Policy Management
- Cybersecurity requirements management.
- Requirements traceability.
- Cybersecurity policies, e.g. access control policy.
- Cybersecurity procedures, e.g. operational and maintenance procedures.
Training
Training & Awareness
- Cybersecurity training for corporate employees.
- Cybersecurity awareness programmes for corporates.
- Cybersecurity training for colleges and universities.
- Cybersecurity course content review as per the latest industry trends.
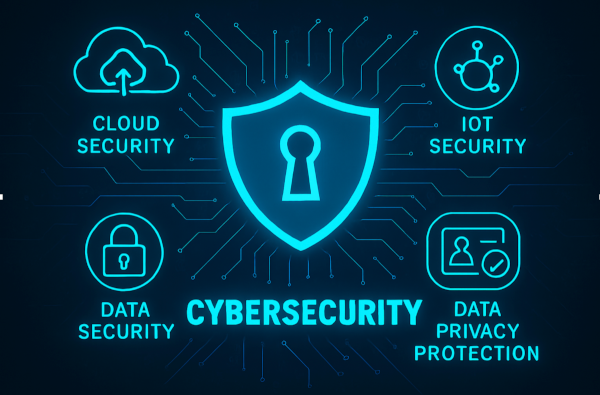
Domains
Emerging Domains
- Cloud security
- IoT security
- Data security
- Data privacy protection
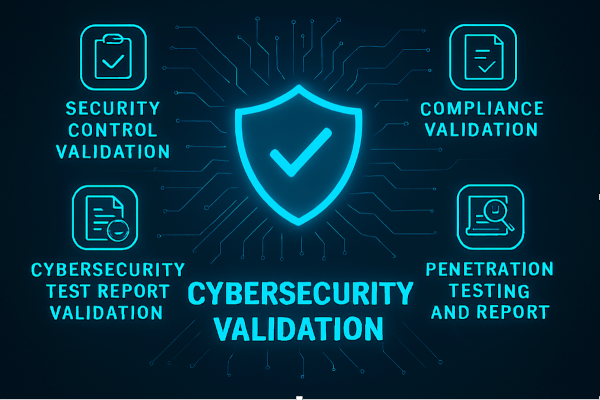
Validation
Cybersecurity Validation
- Security control validation.
- Compliance validation.
- Cybersecurity test report validation.
- Vulnerability assessment and report.
- Penetration testing and report.
Sectors
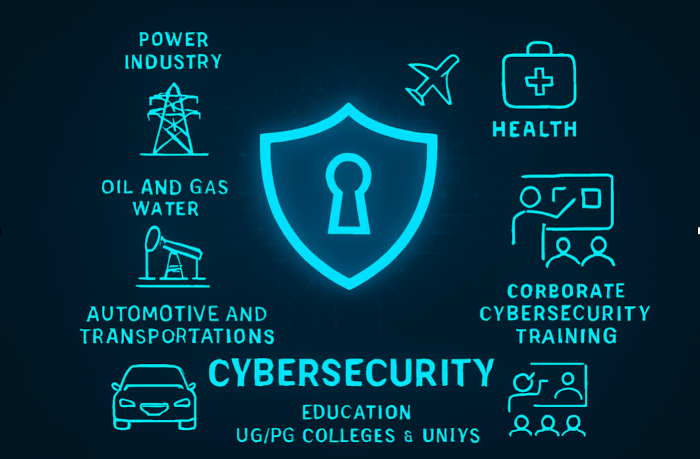
Targeted Service Sectors
- Power industry
- Oil, gas and water
- Automotive and transportation
- Aviation
- Health
- Education — UG/PG colleges and universities
- Corporate cybersecurity training